Fivebar is a free, open-source Windows app that sits between your coding agent and git push. When Claude Code finishes a turn, Fivebar scans the files it changed with three open-source scanners and sends each problem back to the agent with the file, the line and a fix. A pre-push hook stops anything critical or high from leaving your PC. No account, no server, no API key.
Status, 28 October 2026: first release, Windows only, tested with Claude Code on a made-up demo shop app whose problems are planted on purpose. Download the Windows installer. The code is on GitHub: Obiwayne/fivebar (Apache-2.0).
The loop, on a real run
We asked Claude Code for one small feature in a test shop app: "Add a findUserByEmail(email) function to src/users.js." Claude Code wrote a safe version. The file already had three old problems in it: SQL built from a template string, innerHTML set from a variable, and an eval().
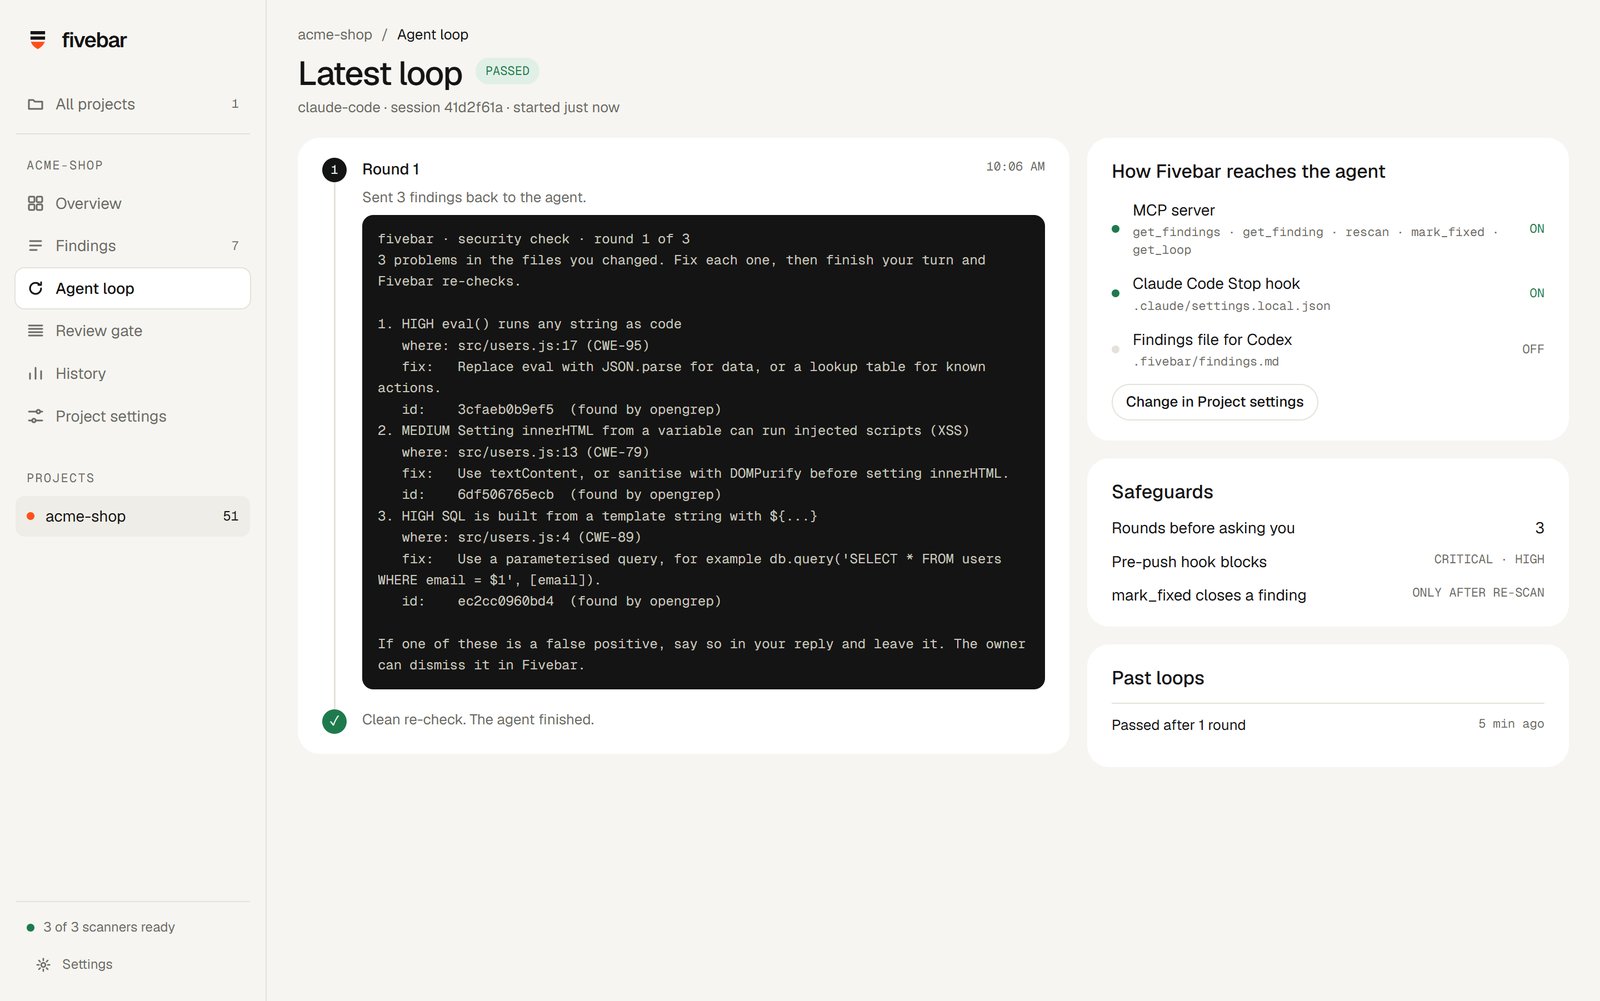
When Claude Code finished its turn, Fivebar's Stop hook scanned the two files it touched and sent this back:
fivebar · security check · round 1 of 3
3 problems in the files you changed. Fix each one, then finish your turn and Fivebar re-checks.

1. HIGH eval() runs any string as code
   where: src/users.js:17 (CWE-95)
   fix:   Replace eval with JSON.parse for data, or a lookup table for known actions.
Claude Code fixed all three in the same session. Fivebar re-checked, closed the findings and marked the loop as passed. We ran the same request three times. Every run took one round and between 40 and 52 seconds from prompt to pass. The project score went from 28 to 51.
If the agent can't fix something in three rounds, Fivebar stops and asks you instead of looping.
What's inside
- Opengrep 1.33.0 (LGPL) runs 12 rules we wrote for JavaScript, TypeScript and Python.
- Gitleaks 8.30.1 (MIT) looks for secrets in files and in the commits you push.
- OSV-Scanner 2.7.0 (Apache 2.0) checks lockfiles against the OSV advisory database.
Fivebar downloads each scanner from its GitHub release and checks it against a pinned SHA-256 before it runs. Results from the three tools are merged, so one problem found by two tools shows up once, with both badges.
The rest is plain Node: an Electron app, a local API on 127.0.0.1 with a random token, SQLite through sql.js so there's nothing native to compile, and an MCP server so the agent can ask for its findings itself. AI work goes through the claude command you already have, on your own Claude plan.
Setting up
Setup is six short steps, one job per screen. You pick your coding agents, Fivebar checks your PC for git and Claude Code, installs the scanners and scans your first project. On the test shop that first scan found 10 problems in 2.6 seconds: two leaked keys, three code issues and five advisories for lodash 4.17.20.
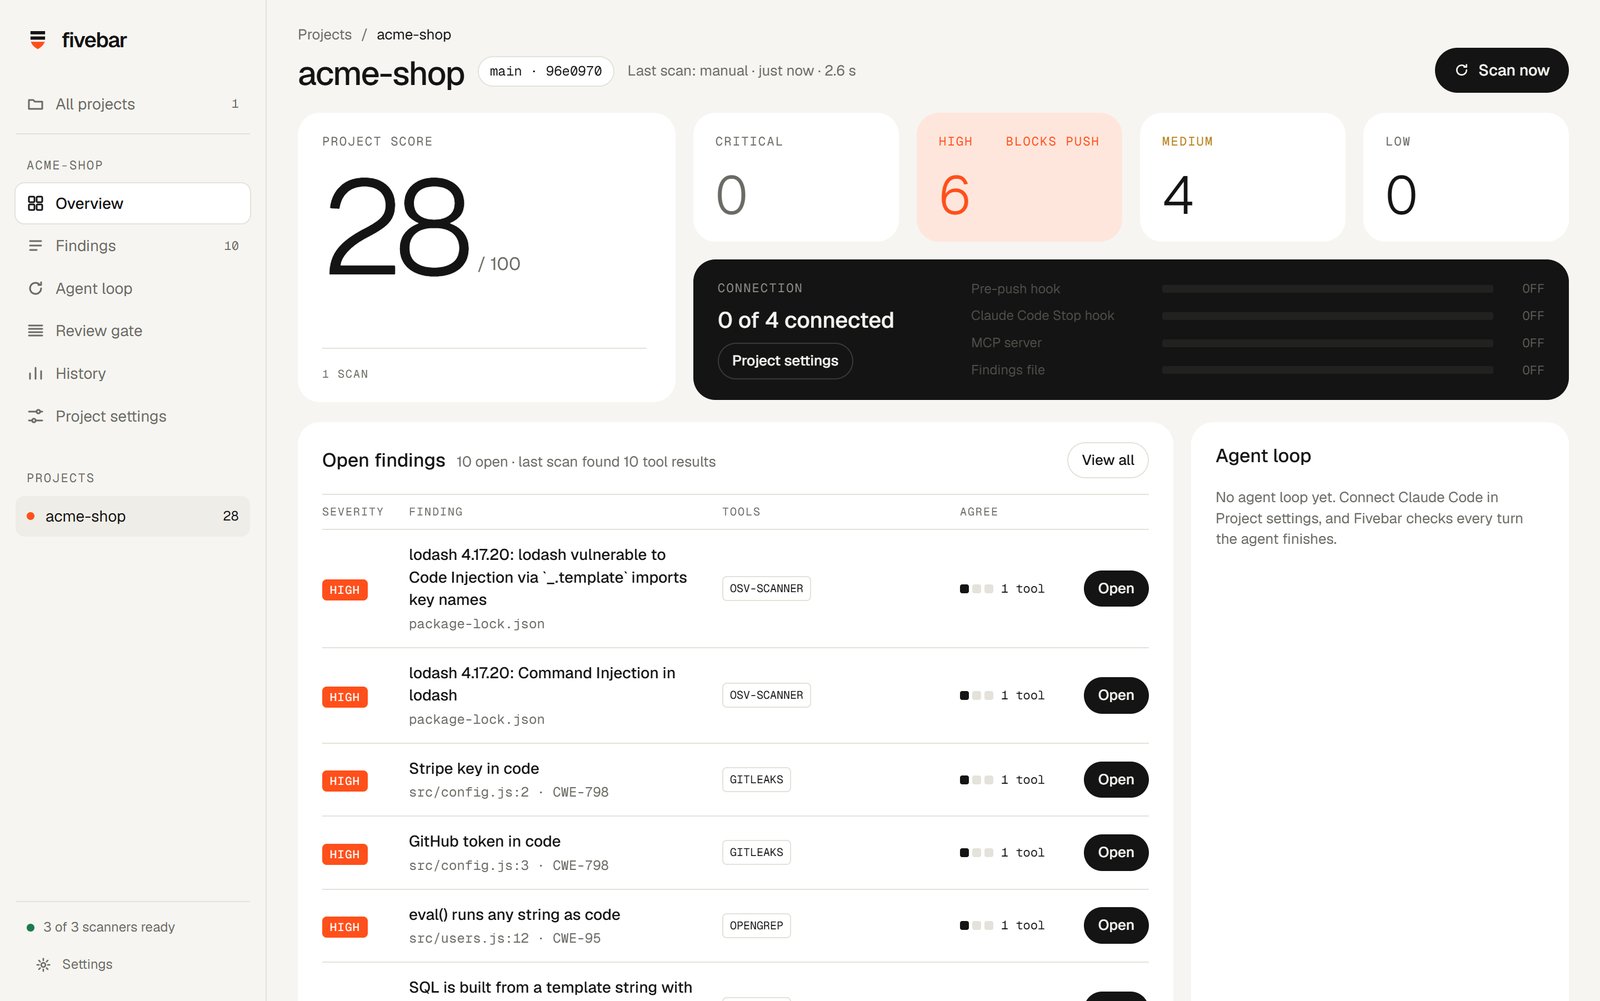
Nothing in your project changes until you press Connect. The Connect screen shows every line Fivebar will write, file by file, before it writes it, and keeps a backup.
The push guard
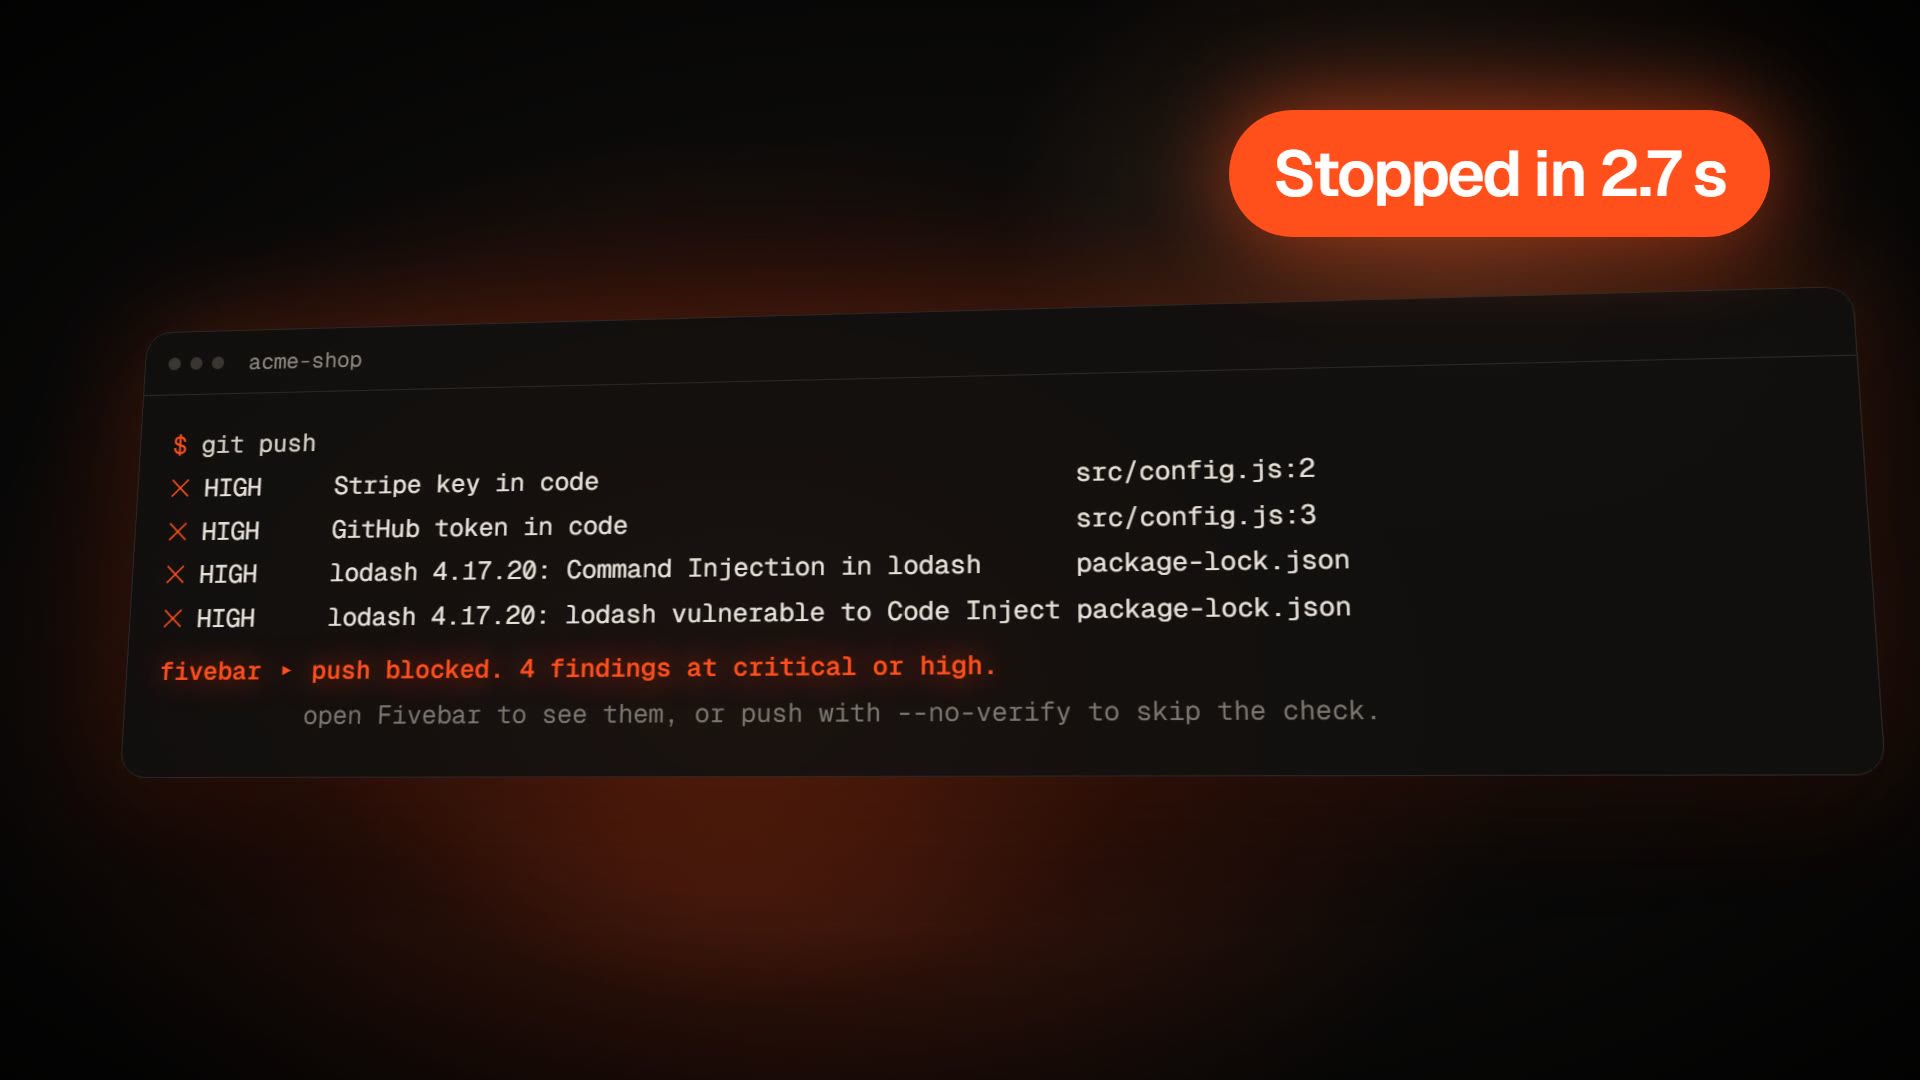
The git pre-push hook scans the files and commits in a push. On the test shop, with the (fake) Stripe and GitHub test keys still in src/config.js, the push stopped in 2.7 seconds:
✕ HIGH     Stripe key in code       src/config.js:2
✕ HIGH     GitHub token in code     src/config.js:3
fivebar ▸ push blocked. 4 findings at critical or high.
Early on, a secret slipped through. We committed a key, deleted it in the next commit, and pushed both. The files looked clean, so the push went through. Gitleaks now scans the commit range being pushed as well, so a secret anywhere in the push history blocks it.
The review gate
The gate scores the latest change from 1 to 5 on security, correctness, readability, tests and maintainability. All five have to be 5. An AI reviewer gives the scores, run through claude -p with read-only tools, and the scanners and your tests set limits it can't score above. A failing test caps correctness at 2. An open high finding caps security at 2.
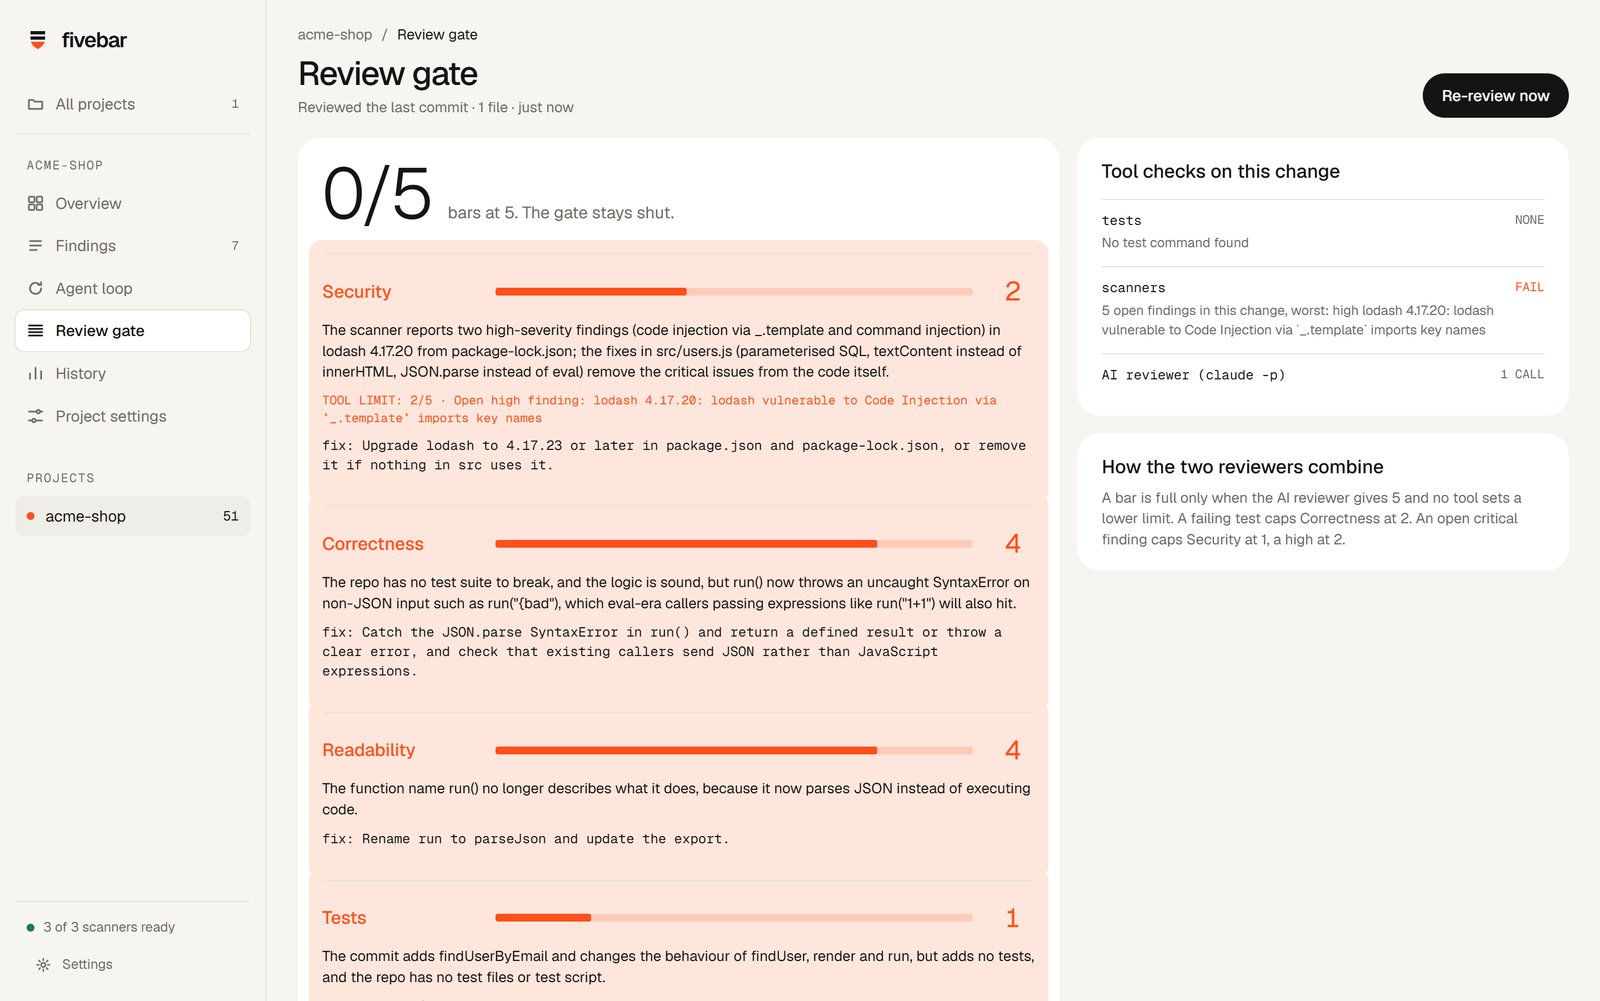
On the shop the gate stayed shut at 0 of 5. The reviewer caught something we'd missed: Claude Code had swapped eval for JSON.parse, so any caller still passing code like run("1+1") now gets an error.
What broke while we built it
Testing on a real setup turned up five problems. We fixed each one before taking these screenshots.
- OSV-Scanner found nothing. The test project sat inside a folder that another repo's
.gitignoreignores, and OSV-Scanner obeys outer.gitignorefiles. Fivebar now checks for that case and passes--no-ignoreonly then. - The agent loop never ran on our PC. The hook was connected and worked when run by hand, but Claude Code never called it. Our own Claude Code settings had
"disableAllHooks": true. Fivebar now reads your Claude Code settings and warns you on the Connect screen when hooks are off. - A message claimed
--no-verifypushes get logged. They don't.--no-verifyskips the hook, so Fivebar never sees the push. We changed the wording. - The review gate said "5 findings in this change" when the change touched one file. The five were lodash advisories, which do count, because the change ships with them. The label now says "5 open (5 in dependencies)".
- The logo vanished on the dark setup screen. The small shield used a fixed dark colour. It now follows the text colour.
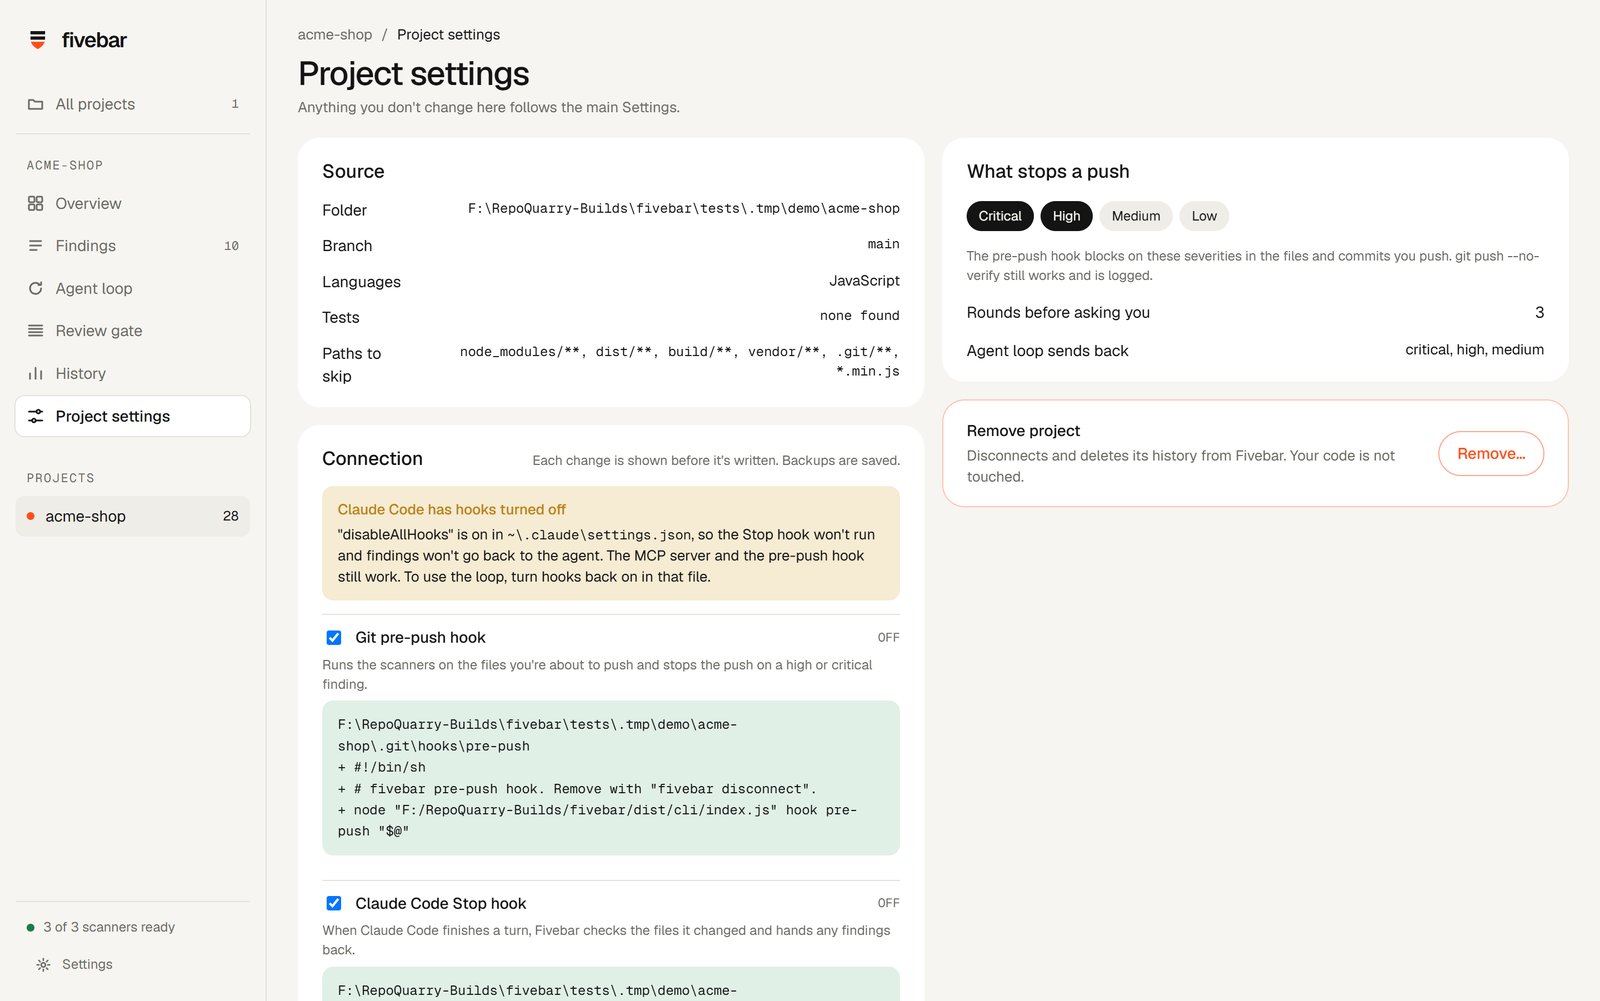
The warning Fivebar shows when Claude Code's hooks are off, added after problem 2.
What it doesn't do
Fivebar checks code on your machine. It doesn't watch live traffic, replace a human review or pen test, or find every bug. The scanners catch known patterns, leaked secrets and published advisories. The review gate adds an AI reviewer's judgement, capped by what the tools found.
What's next
Guards that stop risky commands inside the agent, a nightly scan, a phone app over your own Tailscale network, and direct connectors for Codex and Antigravity. A macOS build needs someone with a Mac. If you'd like to help, the repo is Obiwayne/fivebar, Apache-2.0, and contributors are welcome.
Fivebar is also listed on our Vibe coder's workshop build, next to open-source tools for reviewing what your agent writes.